Cryptography Basics A Complete Guide with Easy Examples
Cryptography is one of the most important technologies used to protect information in the digital world. Every time you send a WhatsApp message, log in to an online account, make an online payment, or visit a website using HTTPS, cryptographic techniques help protect your data.
In simple terms, cryptography is the practice of protecting information by transforming it into a form that unauthorized people cannot understand or use.
This guide explains the basics of cryptography, how it works, its major types, and a simple example.
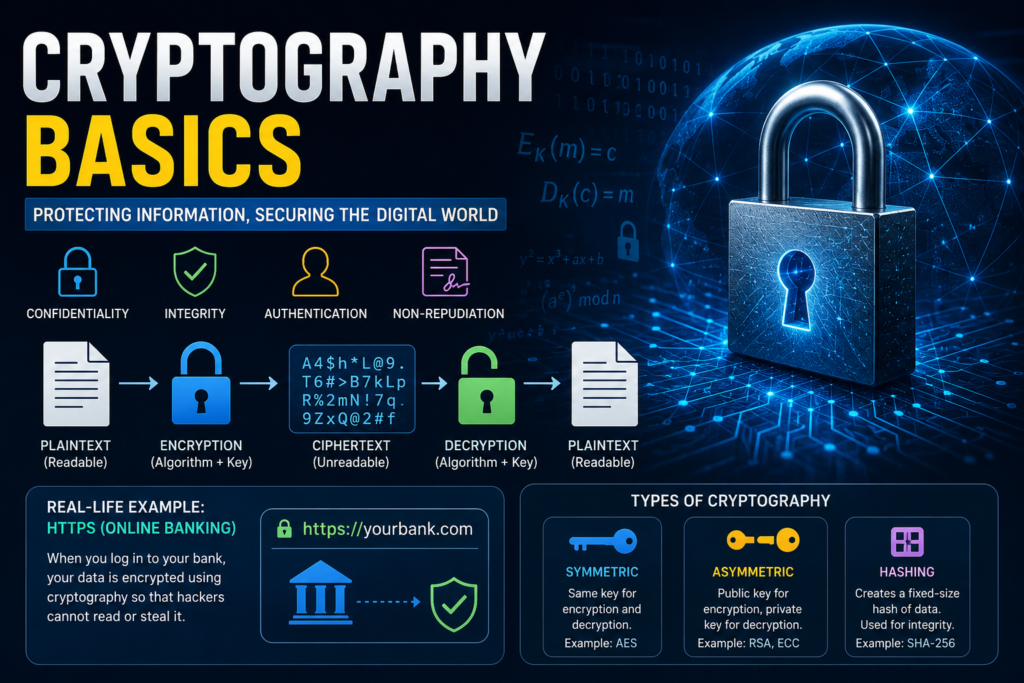
Table of Contents
What Is Cryptography?
Cryptography is a security technique used to protect information from unauthorized access, modification, and misuse.
It commonly involves transforming readable information, called plaintext, into an unreadable format called ciphertext using an algorithm and a cryptographic key.
The basic process looks like this:
Plaintext → Encryption → Ciphertext → Decryption → Plaintext
For example:
Original Message:
Meet me at 5 PM
↓ Encryption
Encrypted Data:
8fA@29xK#pL7…
↓ Decryption
Original Message:
Meet me at 5 PM
Without the appropriate key, an attacker should not be able to recover the original information efficiently.
Why Is Cryptography Important?
Modern systems exchange enormous amounts of sensitive information. Without appropriate cryptographic protection, attackers could potentially intercept or manipulate data.
Cryptography helps provide several important security properties:
1. Confidentiality
Confidentiality ensures that only authorized people can access the information.
For example, when you send a private message, encryption helps prevent an unauthorized person who intercepts the communication from reading its contents.
2. Integrity
Integrity ensures that information has not been modified without authorization.
For example, if a file is changed while being transferred, cryptographic integrity mechanisms can help detect the alteration.
3. Authentication
Authentication helps verify the identity of a person, device, server, or service.
For example, cryptographic protocols help your browser verify that it is communicating with the intended HTTPS website.
4. Non-Repudiation
Non-repudiation provides evidence that a particular party performed an action, particularly through mechanisms such as digital signatures.
Digital signatures can help prove who signed a document and whether the document was changed afterward.
Important Cryptography Terms
Before learning the different types of cryptography, it is useful to understand some basic terminology.
Plaintext
Plaintext is the original readable information.
Example:
My password is Secure123
Ciphertext
Ciphertext is the transformed, generally unreadable result produced by encryption.
Example:
X7#kP91@Lm…
Encryption
Encryption converts plaintext into ciphertext.
Plaintext → Encryption → Ciphertext
Decryption
Decryption converts ciphertext back into its original readable form.
Ciphertext → Decryption → Plaintext
Key
A cryptographic key is information used by a cryptographic algorithm to perform encryption, decryption, signing, or verification.
The security of a cryptographic system should depend on properly protecting the key, not on keeping the algorithm secret.
How Does Cryptography Work?
Consider Alice and Bob.
Alice wants to send a confidential message to Bob.
Alice
|
| Plaintext
↓
Encryption + Key
|
↓
Ciphertext
|
| Internet
↓
Decryption + Key
|
↓
Bob
An attacker may intercept the ciphertext during transmission, but strong cryptography is designed to prevent the attacker from recovering the protected information without the necessary key.
Types of Cryptography
There are three major concepts you should understand:
- Symmetric-key cryptography
- Asymmetric-key cryptography
- Hash functions
Each has a different purpose.
1. Symmetric Key Cryptography
In symmetric cryptography, the same secret key is used to encrypt and decrypt data.
Same Secret Key
↓
Plaintext → Encryption → Ciphertext
↓
Decryption
↓
Plaintext
Example
Suppose Alice and Bob both securely possess the same secret key.
Alice encrypts:
Hello Bob
The result might look like:
9fA72xQ…
Bob uses the same secret key to decrypt the ciphertext.
Common Symmetric Algorithms
Examples include:
- AES (Advanced Encryption Standard)
- ChaCha20
AES is widely used for protecting data at rest and data in transit.
Advantages
- Fast
- Efficient for large amounts of data
- Suitable for files, databases, storage, and network traffic
Disadvantage
The biggest challenge is securely sharing the secret key.
If an attacker obtains the key, they may be able to decrypt information protected with that key.
2. Asymmetric Key Cryptography
Asymmetric cryptography uses a key pair:
- Public key
- Private key
The public key can generally be shared, while the private key must be protected.
A simplified representation is:
Public Key → Can be shared
Private Key → Must remain secret
Asymmetric cryptography is commonly used for:
- Secure key establishment
- Digital signatures
- Authentication
- Certificates
- Secure communication protocols
Examples
Common public key cryptographic systems include:
- RSA
- Elliptic Curve Cryptography (ECC)
- Ed25519
- ECDSA
- Diffie Hellman and elliptic curve variants for key agreement
Symmetric vs. Asymmetric Cryptography
| Feature | Symmetric | Asymmetric |
| Keys | Usually one shared secret | Public/private key pair |
| Speed | Very fast | Generally slower |
| Large data | Excellent | Usually not used directly |
| Key distribution | More challenging | Public key can be distributed |
| Digital signatures | No | Yes |
| Examples | AES, ChaCha20 | RSA, ECC, Ed25519 |
Modern secure systems often use both.
For example, HTTPS can use public key cryptography to establish or authenticate a secure session and then use efficient symmetric cryptography to protect the actual application data.
3. Hash Functions
A cryptographic hash function is different from encryption.
Hashing takes input data and produces a fixed size output called a hash value or digest.
Input
↓
Hash Function
↓
Hash / Digest
For example:
Hello World
↓
SHA-256
↓
A591A6D40BF420404A011733CFB7B190…
A secure cryptographic hash function is designed to make it computationally infeasible to recover the original input from the hash.
Common Hash Functions
Examples include:
- SHA-256
- SHA-512
- SHA-3
Older algorithms such as MD5 and SHA-1 should not be used for modern security sensitive applications because they have known collision weaknesses.
Encryption vs. Hashing
A common beginner mistake is to think encryption and hashing are the same.
They are not.
| Encryption | Hashing |
| Designed to protect data confidentiality | Designed to produce a data fingerprint |
| Reversible with the appropriate key | Designed to be one way |
| Produces ciphertext | Produces a digest |
| Used for confidential data | Used for integrity checks and other security purposes |
For example, encrypted data can be decrypted with the correct key.
A cryptographic hash is not intended to be “decrypted.”
How Are Passwords Protected?
Websites should not store users’ passwords as ordinary plaintext.
Instead, password storage should use a password hashing function designed specifically for passwords, such as:
- Argon2id
- bcrypt
- scrypt
A unique random salt is also used.
Conceptually:
Password + Unique Salt
↓
Password Hashing
↓
Stored Hash
When the user logs in, the submitted password is processed again and compared with the stored password hash.
A general purpose hash such as SHA-256 alone is not an appropriate password storage solution.
Example: Online Banking
Let’s understand cryptography through a familiar real world scenario.
Suppose you open your bank’s website:
You enter:
Username: Ali123
Password: ********
and log in.
Several security mechanisms can be involved.
Step 1: Your Browser Connects to the Bank
Your browser establishes a secure HTTPS connection with the bank’s server.
HTTPS uses TLS (Transport Layer Security).
The server presents a digital certificate that helps the browser authenticate the server’s identity.
Step 2: Cryptographic Handshake
The browser and server perform a TLS handshake.
Modern TLS uses public key cryptography and key agreement mechanisms to establish shared session keys securely.
Step 3: Session Encryption
Once the secure session is established, application data is typically protected using efficient symmetric authenticated encryption.
For example, TLS 1.3 commonly uses algorithms such as:
- AES-GCM
- ChaCha20-Poly1305
Step 4: Your Login Data Is Protected
Your credentials travel through the encrypted TLS connection rather than being sent as ordinary readable HTTP data.
An attacker monitoring the network may see encrypted traffic, but strong TLS encryption is designed to prevent them from simply reading the contents.
Step 5: The Server Verifies Your Password
The bank should securely store your password using an appropriate password hashing scheme rather than storing the original password in plaintext.
Another Simple Example: WhatsApp Messaging
Imagine you send this message:
“Where are you?”
The message is protected by cryptographic mechanisms as it travels between the communicating parties.
Instead of transmitting the message as ordinary readable text, secure messaging systems use encryption to protect the communication.
In end to end encrypted systems, the intended endpoints are designed to be the parties that can decrypt the message contents.
This demonstrates an important principle:
Encryption protects information by making it computationally impractical for unauthorized parties to understand the protected data.
Digital Signatures
Cryptography is not only about hiding information.
It can also prove that data was signed by a particular private key and has not been modified after signing.
A simplified process is:
Document
↓
Hash
↓
Digital Signature + Private Key
↓
Signed Document
The recipient can use the corresponding public key to verify the signature.
Digital signatures are commonly used for:
- Software packages
- Electronic documents
- Certificates
- Secure communications
- Code signing
Cryptography in HTTPS
When you see:
https://
your browser is using HTTPS, which is HTTP protected by TLS.
TLS provides cryptographic protections for communication between your browser and the server.
It helps provide:
- Confidentiality
- Integrity
- Server authentication
This is why HTTPS is essential for modern websites, especially websites handling passwords, payments, personal information, or other sensitive data.
Cryptography in Everyday Life
You may use cryptography every day without realizing it.
Examples include:
- Online banking
- WhatsApp and other secure messaging applications
- HTTPS websites
- Online shopping
- Digital signatures
- VPN connections
- Wi-Fi security
- Password storage
- Secure cloud storage
- Software updates
- Electronic payments
- Authentication systems
Common Cryptography Mistakes
Beginners often make several mistakes when implementing cryptography.
1. Creating Your Own Encryption Algorithm
Do not invent your own cryptographic algorithm for real security applications.
Use well-studied, standardized algorithms and established libraries.
2. Hard Coding Secret Keys
Never expose sensitive cryptographic keys in publicly accessible source code.
3. Using Weak Algorithms
Avoid obsolete algorithms such as:
DES
3DES
RC4
MD5
SHA-1
for new security sensitive applications.
4. Using Weak Password Hashing
Do not store passwords using:
MD5(password)
or:
SHA256(password)
alone.
Use a dedicated password hashing function such as Argon2id, bcrypt, or scrypt with proper parameters and unique salts.
5. Reusing Nonces or IVs Incorrectly
Modern authenticated encryption modes often require unique nonces. Incorrect nonce reuse can seriously compromise security.
This is one reason cryptographic libraries should be used rather than implementing cryptographic primitives manually.
Cryptography and Cyber Security
Cryptography is a fundamental component of cyber security.
It helps protect:
Confidentiality
↓
Encryption
Integrity
↓
Hashes / MACs / Authenticated Encryption
Authentication
↓
Certificates / Digital Signatures / MACs
Non Repudiation
↓
Digital Signatures
However, cryptography alone cannot secure an entire system.
A secure system also requires:
- Strong authentication
- Access control
- Secure software development
- Patch management
- Key management
- Secure configuration
- Monitoring
- Backup and recovery
- User awareness
Simple Summary
Cryptography is the science and engineering of protecting information using mathematical algorithms and keys.
The three fundamental concepts to remember are:
Symmetric Cryptography
One shared secret
↓
Fast encryption/decryption
Examples:
AES, ChaCha20
Asymmetric Cryptography
Public Key + Private Key
Examples:
RSA, ECC, Ed25519
Cryptographic Hashing
Data
↓
Hash Function
↓
Fixed size Digest
Examples:
SHA-256, SHA-3
Quantum Cryptography
Quantum cryptography is a security approach that uses principles of quantum mechanics to protect information and detect eavesdropping.
It is different from Post Quantum Cryptography (PQC):
- Quantum cryptography: uses quantum physics to provide security.
- Post quantum cryptography: uses mathematical algorithms designed to remain secure against quantum computers.
How Quantum Cryptography Works
The best known application is Quantum Key Distribution (QKD).
QKD allows two parties to establish a shared secret key while providing a way to detect whether someone has attempted to intercept the quantum communication.
A simplified process:
Alice
│
│ Quantum states
▼
Quantum Channel
│
├──────────────► Eve
│ (attempted interception)
▼
Bob
Alice + Bob
↓
Detect anomalies
↓
Generate shared secret key
↓
Use key for encrypted communication
Why Eavesdropping Can Be Detected
Quantum mechanics has an important property: measuring an unknown quantum state can disturb it.
Therefore, if an attacker tries to intercept certain quantum signals, their measurement can introduce detectable changes.
This is fundamentally different from simply relying on the computational difficulty of a mathematical problem.
Quantum Key Distribution
Two important QKD protocols are:
1. BB84
BB84 was proposed by Charles Bennett and Gilles Brassard in 1984.
It uses quantum states to allow Alice and Bob to establish a shared secret key and detect potential interception.
2. E91
E91, proposed by Artur Ekert, uses quantum entanglement as part of the key-distribution process.
Quantum Cryptography vs Traditional Cryptography
| Feature | Traditional Cryptography | Quantum Cryptography |
| Foundation | Mathematics | Quantum mechanics |
| Example | AES, RSA, ECC | BB84, E91 |
| Eavesdropping detection | Depends on protocol/implementation | Can exploit quantum measurement properties |
| Requires quantum hardware? | Usually no | For QKD |
| Current deployment | Very widespread | More specialized |
| Main application | Encryption, authentication, signatures | Secure key distribution |
Quantum Cryptography vs Post Quantum Cryptography
This distinction is particularly important:
| Quantum Cryptography | Post Quantum Cryptography | |
| Uses quantum physics? | Yes | No |
| Designed for quantum computers? | Uses quantum phenomena | Yes |
| Requires specialized quantum hardware? | Often, for QKD | No |
| Works over conventional networks? | Not necessarily | Yes |
| Examples | BB84, E91 | ML-KEM, ML-DSA, SLH-DSA |
Simple Example
Think of PQC as building a stronger lock that a future quantum computer cannot easily break.
Think of QKD as using a special quantum communication system where an attempted interception can leave detectable evidence.
Advantages
- Can provide strong security properties for key distribution
- Eavesdropping attempts can potentially be detected
- Based on fundamental quantum mechanical properties
- Useful for certain high security communication environments
Limitations
Quantum cryptography is not a replacement for all cybersecurity.
QKD can require:
- Specialized hardware
- Dedicated optical/quantum communication infrastructure
- Careful implementation
- Protection of endpoints and classical communication channels
It also does not automatically solve problems such as malware, stolen credentials, insecure applications, or compromised endpoints.
Key Takeaway
Quantum cryptography uses quantum mechanical principles to secure communication, particularly through Quantum Key Distribution (QKD).
For your cybersecurity notes, remember:
Quantum Cryptography → Quantum Mechanics → QKD → BB84 → E91 → Detectable Eavesdropping
And:
PQC → Classical Mathematics → Quantum Resistant Algorithms → ML-KEM / ML-DSA
Symmetric and Asymmetric Cryptography
Cryptography protects information by converting plaintext into ciphertext so unauthorized people cannot read it. Two fundamental approaches are symmetric cryptography and asymmetric cryptography.
1. Symmetric Cryptography
Symmetric cryptography uses the same secret key for encryption and decryption.
How it works
Plaintext
↓
Secret Key + Encryption
↓
Ciphertext
↓
Same Secret Key + Decryption
↓
Plaintext
For example, if Alice encrypts a file using a secret key, Bob needs the same key to decrypt it.
Common symmetric algorithms
- AES Advanced Encryption Standard
- ChaCha20
- 3DES legacy/deprecated for most new applications
- DES obsolete and insecure
Advantages
- Very fast
- Efficient for large amounts of data
- Strong security when modern algorithms and appropriate key sizes are used
- Relatively low computational overhead
Main disadvantage
The biggest challenge is secure key distribution.
If Alice needs to send the secret key to Bob over an insecure network, an attacker could potentially steal the key.
2. Asymmetric Cryptography
Asymmetric cryptography, also called public key cryptography, uses a pair of mathematically related keys:
- Public key — can be shared openly
- Private key — must be kept secret
How it works
A simplified encryption example:
Message
↓
Bob’s Public Key
↓
Encrypted Message
↓
Bob’s Private Key
↓
Original Message
Anyone can use Bob’s public key to encrypt information for Bob, but only Bob’s corresponding private key should be able to decrypt it.
Common asymmetric algorithms
- RSA
- Elliptic Curve Cryptography (ECC)
- Ed25519 — commonly used for digital signatures
- ECDSA — digital signatures
- Diffie-Hellman / ECDH — key agreement
Important: not every asymmetric algorithm is primarily an encryption algorithm. Some, such as Ed25519 and ECDSA, are primarily used for digital signatures, while Diffie Hellman variants are used for key agreement.
Symmetric vs Asymmetric Cryptography
| Feature | Symmetric | Asymmetric |
| Keys | One shared secret key | Public + private key |
| Speed | Fast | Generally slower |
| Large data | Excellent | Usually inefficient |
| Key distribution | More difficult | Easier |
| Digital signatures | No | Yes |
| Examples | AES, ChaCha20 | RSA, ECC, Ed25519 |
| Main use | Data encryption | Key exchange, authentication, signatures |
Example: HTTPS
HTTPS commonly uses both approaches rather than choosing only one.
A simplified process is:
Asymmetric Cryptography
↓
Securely establish/authenticate keys
↓
Symmetric Session Key
↓
AES / ChaCha20
↓
Fast encrypted communication
For example, modern TLS can use asymmetric mechanisms such as ECDHE for key agreement and then use a symmetric cipher such as AES-GCM or ChaCha20-Poly1305 to protect the actual data.
Easy way to remember
Symmetric = Same key
One secret key → encryption + decryption
Asymmetric = Two keys
Public key + Private key → public key cryptography
Connection to Post Quantum Cryptography
This is also important for your previous topic. RSA and ECC are vulnerable to sufficiently powerful quantum computers, whereas modern post quantum algorithms such as ML KEM are designed to provide quantum resistant public key key establishment. Symmetric cryptography, such as AES, faces a different and generally less severe quantum threat.
Conclusion
Cryptography is a fundamental technology behind modern digital security. It protects information during communication, helps verify identities, detects unauthorized modifications, and supports secure authentication.
From online banking and HTTPS to secure messaging and digital signatures, cryptographic techniques are working behind the scenes every day.
If you are beginning your journey in cyber security, networking, programming, or ethical hacking, understanding cryptography is essential because many modern security technologies are built on these principles.
Remember the basic flow:
Plaintext
↓
Encryption
↓
Ciphertext
↓
Decryption
↓
Plaintext
And the most important lesson is:
Good cryptography is not about hiding the algorithm; it is about using strong, publicly studied algorithms with properly generated, protected, and managed keys.